Solved

How to test Patient Zero policy is really work or not

  • Mar 13, 2024 1:46 PM UTC
  • 3 replies
  • 331 views

AyyanarG
Forum|alt.badge.img+1

Hi team,


We have created the Patient Zero threat protection policy in my environment, before enabling rule to wider group like to do testing that rule.


could you guide me if anyway to do test in Realtime?
Best answer by Paolo Passeri

Ayyanar, if the file is deemed clean, the user will have to retry a download once the analysis is complete. If the file is benign it will be inserted into a whitelist cache, and the download will be possible.

View original
This topic has been closed for replies.

3 replies

Paolo Passeri
Netskope Employee
Forum|alt.badge.img+11
  • Netskope Employee
  • Mar 28, 2024 4:34 PM UTC

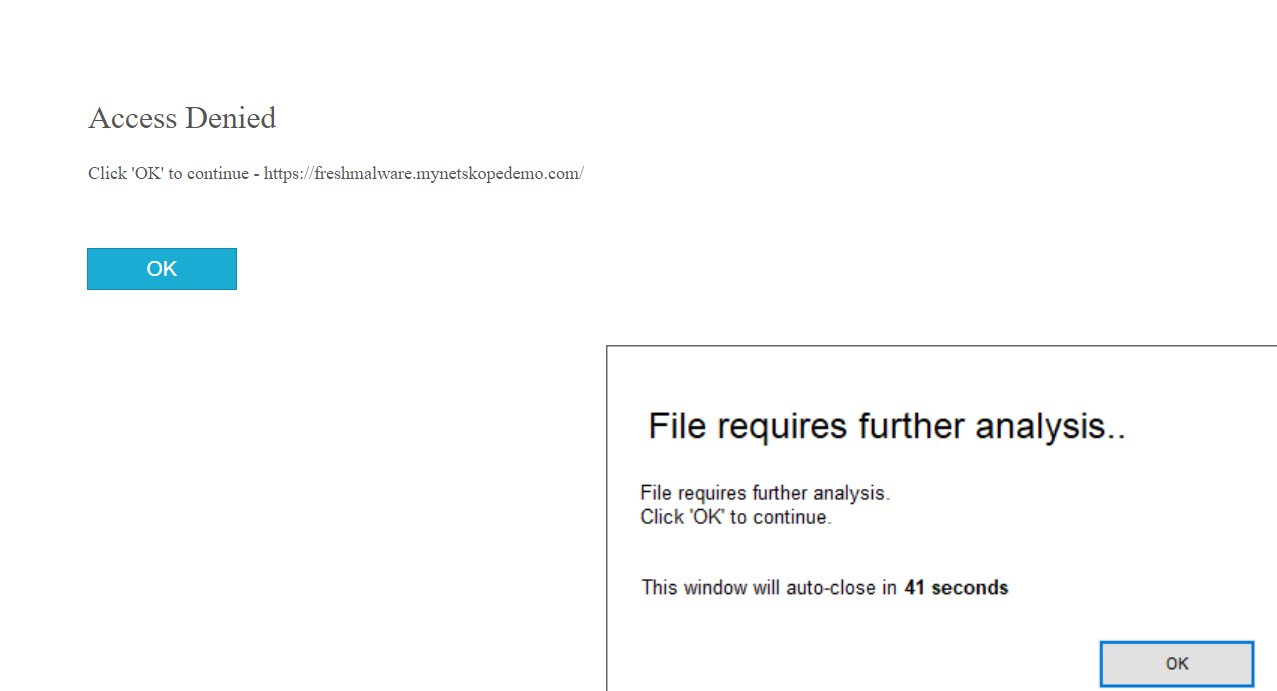
With one of the Netskope steering mechanisms enabled you can visit https://freshmalware.mynetskopedemo.com/ where you will find some samples that trigger the patient zero policy.


AyyanarG
Forum|alt.badge.img+1
  • Author
  • New Member III
  • Mar 28, 2024 5:07 PM UTC

Hi Ppasseri,


Thanks for your answer, yes i tested and able to see its getting trigger showing below screen. If the file is deemed clean by the Netskope threat engine, it will be automatically downloaded? otherwise, users must retry what is the behavior of this rule.


BR

Ayyanar G


Paolo Passeri
Netskope Employee
Forum|alt.badge.img+11
  • Netskope Employee
  • Answer
  • Mar 28, 2024 5:10 PM UTC

Ayyanar, if the file is deemed clean, the user will have to retry a download once the analysis is complete. If the file is benign it will be inserted into a whitelist cache, and the download will be possible.